Blog
Product notes, program guidance, and how Core GRC teams run privacy and risk work.
Blog for South Africa (2 items)
Data Breach Notification Laws: Deadlines and Requirements by Jurisdiction
Who to notify after a personal data breach, how fast and what to say: GDPR, UK, POPIA, US state and federal rules, Canada, Australia, NIS2 and DORA side by side, with a worked…
James Seeliger
What Is Third-Party Risk Management (TPRM)? Lifecycle, Regulations and How to Build a Programme
A practical guide to third-party risk management: what TPRM means, the lifecycle regulators expect, how DORA, NIS2, GDPR, PRA, US banking guidance and POPIA frame it, a maturity…
James Seeliger
SOC 2 Report: What It Contains and How to Review a Vendor's Report
A buyer's guide to the SOC 2 report: the five sections, Type 1 vs Type 2 vs SOC 1 and SOC 3, a 10-step review checklist covering bridge letters, carve-outs, CUECs and exceptions,…
James Seeliger
What Is GRC? Governance, Risk and Compliance Explained
GRC (governance, risk and compliance) explained: the three parts, GRC in cyber security, GRC vs ERM vs IRM, the EU, UK and South African rules that expect it, a maturity model, a…
James Edward Anthony
What Is a DSAR? How to Respond to a Data Subject Access Request
A practical guide to data subject access requests: what a DSAR is, who can make one, response deadlines under GDPR, UK GDPR, POPIA/PAIA and CCPA, an eight-step response process, a…
James Seeliger
Vendor Risk Assessment Questionnaire: 60 Questions by Tier (Free Template)
A free, tiered vendor risk assessment questionnaire: 15 core questions for every supplier, 25 more for medium-risk vendors and 20 for critical ones, each with the evidence to…
James SeeligerVendor Risk Assessment: A Step-by-Step Guide with Scoring Templates
A practical seven-step vendor risk assessment process with an inherent risk tiering matrix, a weighted control scoring model, a worked payroll vendor example and a map of what…
James
What is ADA Compliance in the Digital Space?
Learn what ADA compliance means for websites and digital platforms, how it relates to WCAG Level AA, and why accessible design matters for businesses, users, and legal compliance.
James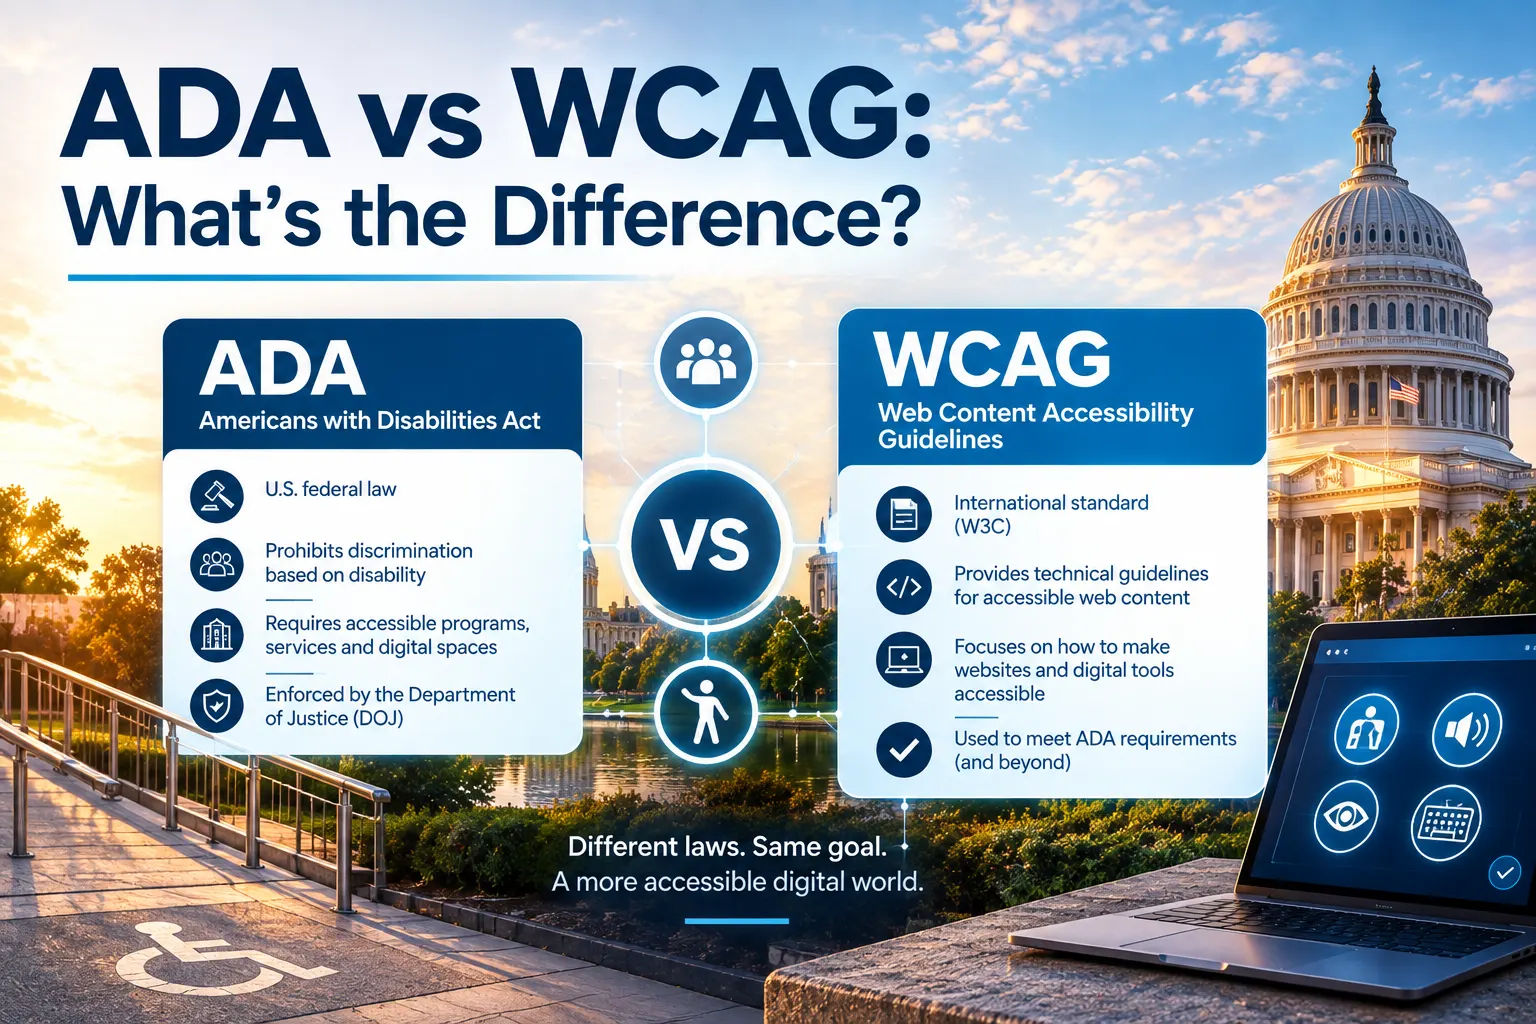
ADA vs WCAG: What's the Difference?
The difference between the ADA and WCAG is their nature: the former is a disability accessibility–related law, while the latter consists of accessibility guidelines.
James
Why Canada's Bill C-27 Died in Parliament: The Background Behind Bill C-36
How Canada's previous privacy reform, Bill C-27 (the Digital Charter Implementation Act), stalled in committee for two years and expired in January 2025.
James
Canada's Bill C-36 Explained: The Protecting Privacy and Consumer Data Act
A comprehensive guide to Canada's Bill C-36 (PPCDA), its new Digital Safety and Data Protection Commission, rules for children's data, automated decisions, and penalties.
James
What is CalPrivacy? A plain-English explanation
CalPrivacy is California’s independent privacy regulator. It administers the CCPA, the Delete Act (including DROP for data brokers), and, from 2027, the Opt Me Out Act.
James
Ready to run risk and privacy in one place?
See the modules that match your program in a short demo. Start with one, add more when you need them.